By Olivia Harper. Fact-checked against 2025–2026 breach and threat reports, Cloud Security Alliance research and public incident reports.
For the first time in Google Cloud’s incident data, flaws in third-party software, not weak passwords, topped the cloud security risks that let attackers in. They opened the door in 44.5% of cases in the second half of 2025, while weak or missing credentials fell to 27.2%.
Many guides on the risks of cloud computing still quote a human-error forecast that expired with 2025. Today’s security concerns in cloud computing include stolen app tokens, phone scams that slip past MFA and hijacked AI keys. Below are 15 risks drawn from real 2025–2026 incidents, each with the first fix to make, building on our cloud security guide.
What Are the Biggest Cloud Security Risks in 2026?
The biggest security risks of cloud computing in 2026 are exploited software flaws, stolen or phished identities, over-privileged machine and AI accounts, compromised third-party apps and quiet data theft. Most incidents start on the customer’s side of the shared responsibility model, not inside the provider’s infrastructure.
Cloud security statistics from outside Google’s data point the same way. Verizon’s 2026 Data Breach Investigations Report reviewed more than 22,000 confirmed breaches across all environments. It found vulnerability exploitation behind 31% of them and credential abuse behind just 13%. Passwords still matter, but attackers now reach for a fresh exploit first.
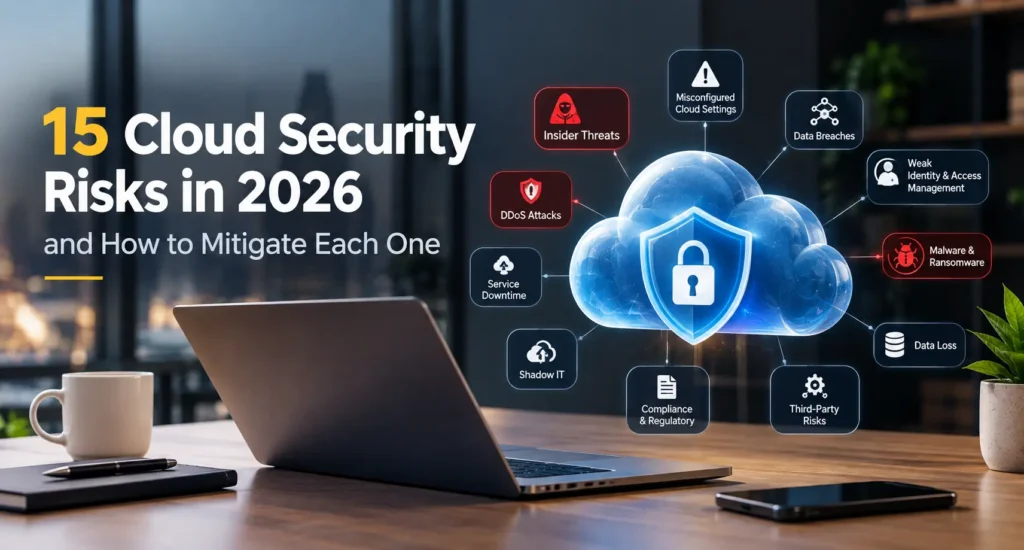
Some of these cloud security threats are new, such as hijacked AI keys and rogue agents. Others are old problems that attackers now exploit faster. Here are the 15 cloud computing security risks covered below, how each one gets abused and where to start:
| # | Risk | How attackers use it | First fix |
|---|---|---|---|
| 1 | Weak and stolen credentials | Sign in with leaked, reused or default passwords | Require passkeys or FIDO2 keys for every admin |
| 2 | Phone scams that get around MFA | Pose as staff to get MFA reset, or trick users into approving a device code | Confirm reset requests by calling back a known number |
| 3 | Machine identities with too much power | Steal a service account key that can reach everything | Swap long-lived keys for short-lived credentials |
| 4 | Misconfigured cloud settings | Scan the internet for public storage and open ports | Block public access with account-wide policies |
| 5 | Exposed APIs and admin panels | Call endpoints that skip authentication | Inventory every endpoint and lock each one behind sign-in |
| 6 | Software flaws exploited within days | Run a public exploit before the patch lands | Patch internet-facing CISA KEV flaws within 72 hours |
| 7 | Stolen OAuth tokens from connected apps | Reuse a SaaS app’s token to pull records in bulk | Review connected apps and revoke unused tokens |
| 8 | Poisoned packages and over-trusted pipelines | Hide code in a dependency, then ride the pipeline’s cloud access | Tie CI/CD cloud trust to one repository and branch |
| 9 | Shadow AI | Staff paste company data into unapproved AI tools | Publish an approved AI list with SSO sign-in |
| 10 | LLMjacking and hijacked resources | Use stolen keys to run AI models or crypto miners on your bill | Set budget alerts and model-access quotas |
| 11 | Over-permissioned AI Agents | Abuse an agent’s broad permissions through its tools or prompts | Give each agent its own read-only identity |
| 12 | Quiet data theft | Copy data slowly through legitimate APIs | Alert on unusual bulk reads and exports |
| 13 | Insiders using personal cloud storage | Sync files to a personal account before leaving | Block personal storage sites on work devices |
| 14 | Ransomware and extortion | Steal data, then threaten to leak it | Keep immutable backups in a separate account |
| 15 | Provider outages and single-region dependence | No attacker needed: one failed region takes you offline | Run critical apps in two regions and test failover |
Which Identity Threats Hit Cloud Accounts Most?
Most cloud threats still end the same way: someone signs in as a person, script or service they aren’t.
1. Weak and Stolen Credentials
In incidents on major cloud and SaaS platforms specifically, Google found identity problems behind 83% of initial access, which is a broader measure than the password-only figure above. Little of that is clever cloud computing hacking. It’s usually one of these:
- A password reused from a breached site
- A default admin login nobody changed
- A session token that infostealer malware lifted from a laptop
How to mitigate it:
- Move admins and finance staff to passkeys or FIDO2 security keys. Attackers can phish SMS codes and push approvals; they can’t phish a hardware-bound key.
- Block legacy sign-in protocols, such as basic authentication for email, which skip MFA entirely.
- Turn on leaked-credential detection, such as the leaked-credentials check in Microsoft Entra ID Protection, and force a reset when it finds a match.
2. Phone Scams That Get Around MFA
Late on a Friday, the help desk takes a call. A “new hire” is locked out, sounds stressed and knows their manager’s name from LinkedIn. A few minutes later, the caller has a fresh MFA device on someone else’s account.
Voice phishing (vishing) like this was the way in for 17% of cases in Google’s data. CrowdStrike’s 2026 Threat Hunting Report adds that:
- Vishing intrusions doubled in the first half of 2026
- Monthly device-code phishing attempts rose fifteenfold in six months. These attacks trick a user into approving an attacker’s sign-in on a genuine login page.
- One group went from account takeover to stolen SaaS data in under five minutes
Reset MFA only after calling back the number already on file, or after a manager confirms through a separate channel. Then use Conditional Access in Microsoft Entra to block device-code sign-in for everyone who doesn’t need it. Most companies need it only for a few shared screens, such as conference-room displays.
3. Machine Identities With Too Much Power
A machine identity is any non-human login that software uses to reach cloud services. Examples include service accounts, API keys, workload roles and CI/CD tokens. They now outnumber employees 82 to 1, according to CyberArk’s 2025 Identity Security Landscape, yet few get the access reviews people do.
IBM’s 2026 Cost of a Data Breach Report found that only 46% of organizations secure the non-human identities inside their AI workflows.
The real danger is one key that never expires and can reach everything. Three steps shrink it:
- Swap stored keys for short-lived credentials. Use workload identity federation through AWS IAM roles, Azure managed identities or Google Cloud Workload Identity Federation.
- Delete keys nobody has used in 90 days. AWS IAM Access Analyzer and similar tools list them for you.
- Grant each workload only the actions it calls, with no wildcards.
How Do Attackers Find a Way Into Cloud Environments?
Stolen logins aren’t the only way in. The next three risks are doors that a scan of the internet can find without anyone’s password.
4. Misconfigured Cloud Settings
Why does a public storage bucket still make the news? AWS has blocked public access on new S3 buckets by default since April 2023, but older buckets, other clouds and one rushed “temporary” change keep the problem alive. Misconfiguration was still the entry point in 21% of the cloud cases Google studied, down from 29.4% six months earlier.
Most cloud storage security issues come down to one setting changed without review. Set guardrails that apply to the whole account rather than to each resource:
- AWS Service Control Policies or Azure Policy rules that deny public access outright
- IaC scanning, such as Checkov on Terraform files, before changes merge
- Continuous posture checks from a cloud security posture management tool, which flag the drift that gets past the first two
5. Exposed APIs and Admin Panels
The trend is improving. Exposed interfaces dropped from 11.8% to 4.9% of cloud entry points in Google’s data in a single half-year. Each one that remains is still a way in: a forgotten /v1 endpoint with no sign-in, or a Jenkins, Grafana or Kubernetes dashboard reachable from any coffee shop.
The fix: List every API and console you run, including old versions; an API gateway’s logs are a good place to start. Require authentication on every endpoint, internal ones included. Move admin panels behind private access, such as a VPN or a zero-trust gateway, so they never face the public internet.
6. Software Flaws Exploited Within Days
Attackers now move faster than most patch cycles. CrowdStrike found that 88% of exploitation involving a public proof of concept happened within 48 hours of its release in the first half of 2026.
Defenders are slipping the other way. Verizon’s 2026 DBIR reports that only 26% of critical flaws in CISA’s Known Exploited Vulnerabilities (KEV) catalog were fully fixed in 2025, and the median fix time grew from 32 to 43 days.
That gap is where a typical cloud attack begins. Close it like this:
- Patch internet-facing systems with KEV-listed flaws within 72 hours, ahead of the normal monthly cycle.
- When a patch can’t ship that fast, add a web application firewall (WAF) rule that blocks the exploit as a stopgap.
- Rank everything else by attack path. A flaw on a public server that holds a powerful role comes first. A platform such as a CNAPP maps those paths for you.
How Do Connected Apps and Suppliers Create Cloud Security Issues?
Your cloud security is only as strong as everything you’ve plugged into it. Verizon’s 2026 DBIR found a third party involved in 48% of breaches, up from 30% a year earlier. That makes partner apps and open-source code some of the fastest-growing cloud services security issues.
7. Stolen OAuth Tokens From Connected Apps
In August 2025, a group Google tracks as UNC6395 stole OAuth tokens from Drift, a Salesloft chatbot connected to many companies’ Salesforce accounts. The tokens let the attackers skip passwords and MFA and export Salesforce records directly.
Google said more than 700 organizations were potentially affected, including several well-known security companies. The attackers then searched the stolen records for AWS access keys, passwords and Snowflake tokens to reach even more systems.
Few cloud security examples show the chain reaction this clearly: one integration led to hundreds of CRMs, which led to the cloud keys people had pasted into support tickets. To cut that chain:
- List every connected app in Salesforce, Microsoft Entra and Google Workspace, and remove the ones nobody uses.
- Give each token the narrowest scope it needs, and restrict tokens to known IP ranges where the platform allows it.
- Alert on bulk exports and unusual API volume from integration accounts.
- Never store credentials in CRM notes or tickets. That data is exactly what attackers search first.
8. Poisoned Packages and Over-Trusted Build Pipelines
Google described one 2025 incident that started with a single bad package: Compromised npm package (QUIETVAULT) → stolen GitHub token → abused GitHub-to-AWS trust → full cloud compromise in 72 hours
The malware even used an AI model running on the developer’s machine to hunt for config files. It’s not a one-off. CrowdStrike found that npm packages made up 87% of malicious software-registry threats so far in 2026.
The weak link was the trust between GitHub and AWS, which uses OpenID Connect (OIDC). Tighten it at each link:
- Limit OIDC trust. In the AWS role’s trust policy, allow only one repository and branch (for example, repo:your-org/app:ref:refs/heads/main), never a whole organization.
- Lock dependencies. Commit lockfiles, install with npm ci, and block install scripts where your builds don’t need them.
- Scan before you merge. Tools such as Dependabot or OSV-Scanner flag known-bad and newly compromised packages.
What New Cloud Risks Did AI Bring in 2026?
AI created cloud computing concerns that barely existed two years ago. These risks involve people, stolen keys and software agents, each in its own way.
9. Shadow AI
Shadow AI played a part in 43% of the breaches in IBM’s 2026 Cost of a Data Breach Report, up from 20% the year before. The cause is usually ordinary. Verizon’s 2026 DBIR found that 67% of AI users on company devices signed in with personal accounts, so prompts, files and customer data end up in tools your security team can’t see.
Banning AI rarely works; people just hide it better. Publish a short list of approved AI tools, make them easy to reach, and require sign-in through company SSO so usage stays visible and you can revoke access when someone leaves.
10. LLMjacking and Hijacked Cloud Resources
LLMjacking means stealing cloud credentials to run expensive AI models on someone else’s account. CrowdStrike’s 2026 Threat Hunting Report describes one attacker who sent nearly 200,000 API requests to a model service in two minutes.
Hijacked cloud resources, whether AI models or crypto miners, can run up unauthorized charges from $10,000 to more than $100,000. The victim usually learns about it from the invoice.
Stop it early:
- Set budget alerts and cost anomaly detection, such as AWS Budgets and Cost Anomaly Detection, at the account level.
- Use policies to deny AI model calls in accounts and regions that don’t need them, and cap request quotas where you do.
- Keep model API keys out of code, store them in a secrets manager, and rotate them on a schedule.
11. Over-permissioned AI agents
Who approved what the agent just deleted? Teams now connect AI agents to cloud consoles, ticketing systems and databases through tools such as Model Context Protocol (MCP) servers, often using a shared admin token. If a poisoned prompt or a buggy tool call goes wrong, nobody can tell the agent’s actions apart from a person’s.
IBM found that 92% of organizations that had an AI-related incident lacked proper AI access controls. Three rules change that:
- Separate identity: give every agent its own identity, never a borrowed human or admin account, so its actions appear separately in logs.
- Read-only first: start each agent with read-only permissions and add write access one action at a time.
- A human in the loop: require a person to approve destructive steps such as deletes, permission changes and payments.
Which Risks Put Your Data and Uptime on the Line?
The last four risks are about what happens to your data after someone gets in, and what happens when the cloud itself goes down.
12. Quiet Data Theft
Data was the target in 73% of the cloud incidents Google studied, and silent theft or espionage was the attacker’s goal in 45%. These breaches set off few alarms because the data leaves through normal APIs, a little at a time. IBM adds that 53% of breached organizations hadn’t encrypted their sensitive data both at rest and in transit, which turned a break-in into a costly loss.
Cloud data breaches of this kind need alerts that track how much data leaves, and how fast:
- Encrypt sensitive stores with customer-managed keys. A stolen copy is useless without access to the key.
- Alert on bulk reads, large exports and first-time access to sensitive buckets or tables.
- Limit egress so production workloads can reach only the destinations they need.
Each step reduces a different data security risk: exposure, slow detection and easy exfiltration.
13. Insiders Moving Data to Personal Cloud Storage
Two weeks after giving notice, a sales manager drags the “Clients” folder into a personal cloud drive “for reference.” Nothing gets hacked, and nobody notices.
That’s the most common insider story in Google’s data: 909 of 1,002 insider cases (91%) involved data exfiltration. Cloud services are the fastest-growing route out, on track to overtake email.
It’s one of the biggest security concerns with cloud storage, and it’s mostly a policy problem. Block personal storage sites on managed devices with your secure web gateway or CASB. Then revoke access on the day someone leaves, not at the end of the week.
14. Ransomware and Extortion
Here’s a myth worth dropping: most cloud attackers don’t bother encrypting anything. Ransomware was the goal in only 3% of Google’s cloud cases, while extortion (steal the data, then threaten to leak it) reached 28%.
Ransomware still hit 39% of organizations overall in IBM’s 2026 data. Your defense is immutable backups, such as S3 Object Lock or Azure immutable blob storage, kept in a separate account the attacker can’t reach.
15. Provider Outages and Single-Region Dependence
On October 20, 2025, a flaw in the automation that manages DNS records for Amazon DynamoDB left its endpoint in AWS’s us-east-1 region with an empty address.
The failure cascaded across services, and some customers felt the impact for about 15 hours. No attacker was involved, yet apps from games to banks went dark.
So what are the risks of using a cloud service provider? Mostly this kind of concentration risk, which rarely shows up among other cloud service security concerns. To reduce it:
- Run your most critical apps in at least two regions, and test failover every quarter.
- Map which SaaS tools you rely on and check whether they depend on a single region.
- Keep a manual fallback, such as status pages and contact lists, outside the provider.
Which Cloud Security Problems Should You Fix First?
You can’t fix 15 risks in a month, and you don’t have to. Most problems with cloud computing security share one root cause: access that’s broader, older or more public than it needs to be. Start where attackers get in most often and where the fix costs the least. The challenges of cloud computing change as you grow, so your first 30 days depend on team size:
| Team size | First 30 days | Why these first |
|---|---|---|
| Small team (one cloud, a few people handling IT) | Passkeys for admins (#1), delete unused keys (#3), budget alerts (#10), patch internet-facing KEV flaws (#6) | Mostly free, and together they close the most common ways in |
| Growing team (several apps, frequent releases) | Review connected apps (#7), lock down build-pipeline trust (#8), turn on continuous posture checks (#4) | Integrations and pipelines multiply faster than anyone reviews them |
| Large organization (multiple clouds and business units) | Attack-path analysis (#6), separate identities for AI agents (#11), tested multi-region failover (#15) | At scale, the hard parts are knowing what to fix first and staying online |
After the first month, work down the rest of the list. Past that point, the real cloud security challenges are keeping pace with change and covering every account.
Our cloud security tips and best practices guide covers the everyday habits that keep these risks from coming back. If you’re unsure whether posture checks are enough or you need full attack-path coverage, our CNAPP vs CSPM comparison walks through that decision.
FAQ’s
What is the single biggest security risk in cloud computing?
Identity. Stolen, phished or over-privileged accounts sit behind more cloud incidents than any other cause.
The Cloud Security Alliance’s Top Threats Deep Dive 2025 traced eight real breaches and found the same pattern behind most cloud computing and security issues: weak identity controls, repeated misconfigurations and supply-chain gaps.
What’s the difference between a cloud security risk, a threat and an issue?
- A threat is who or what could cause harm, such as an attacker, an insider or an outage.
- An issue, or vulnerability, is a weakness in your own setup, such as a public bucket or an old access key.
- A risk is the chance that a threat exploits an issue, weighted by the damage it would cause.
Who is responsible for cloud security, the provider or the customer?
Both, under the shared responsibility model. AWS, Microsoft Azure and Google Cloud secure the physical data centers, hardware and core services.
You secure everything you configure: identities, data, network rules, applications and connected apps. The one risk you can only plan around is a provider outage.
How secure is cloud computing in 2026?
The infrastructure of the major providers is rarely where breaches start. So how secure is cloud computing? It’s as secure as the way you set it up and sign in to it.
Teams that use phishing-resistant MFA, short-lived credentials and tested backups are often safer in the cloud than in their own server room. Teams that skip those basics aren’t.
How often should you review cloud security risks?
Check identities, posture and unusual activity continuously with automated alerts. Each month, review connected apps, unused keys and the AI tools people actually use.
Run a full assessment once a year, and again after any major change, such as adding a new cloud, an acquisition or deploying AI agents. That’s when new security challenges in cloud computing tend to appear.